From purchasing hardware in Switzerland to our secure Good-ID offices, every link is designed to protect your data. Good-ID acts as a processor (GDPR, art. 28), within a strict technical, contractual and human framework — for outsourcing you can entrust with complete confidence.
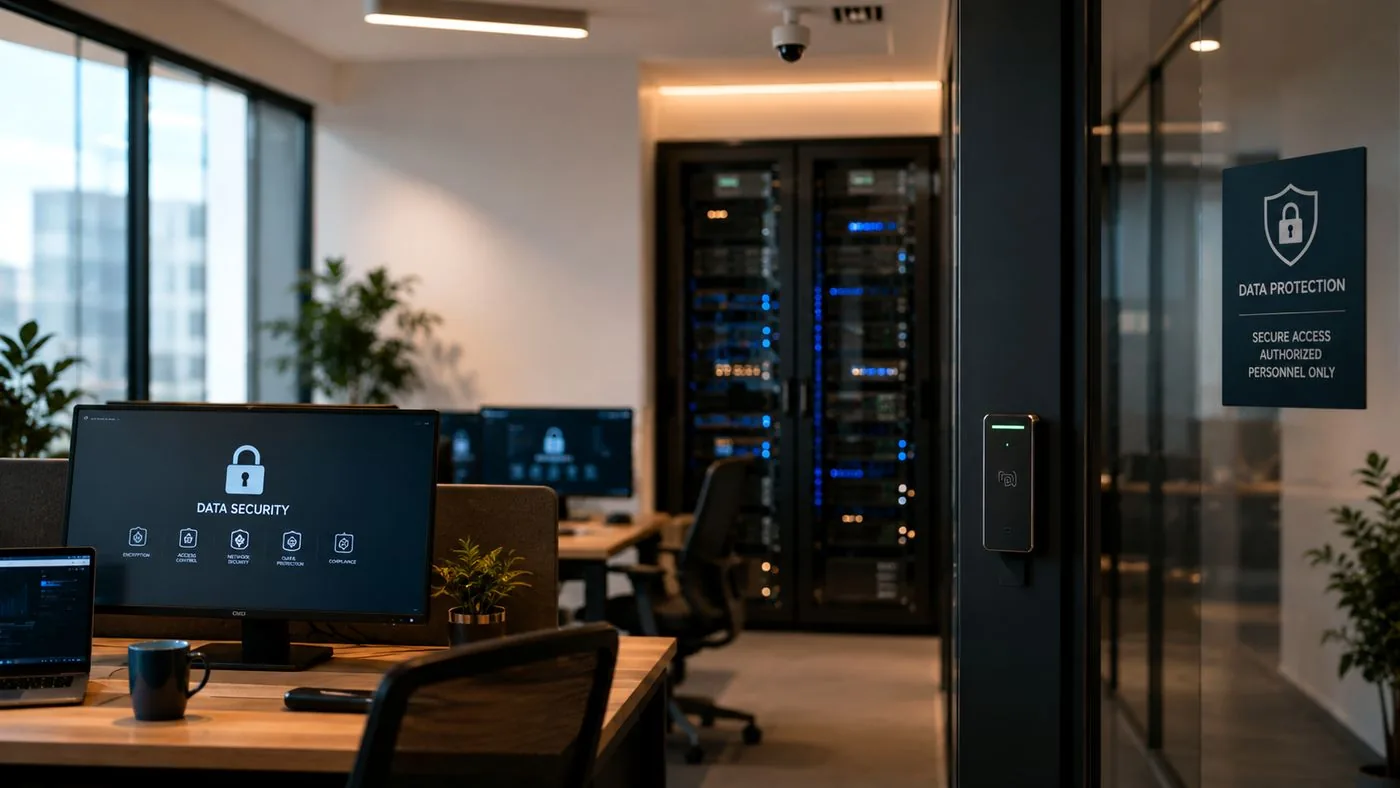
A setup designed upfront, from Switzerland to our offices.
Hardware, software, network and premises: everything is designed and controlled so that no data leaves our perimeter.
Computers bought new and configured in Switzerland. Accounts are set up remotely: the user knows only a PIN code, changeable from Switzerland to lock a workstation at any time.
Software installed from Switzerland, private browsing and third-party browsers blocked (a single authorised browser), remote control. Auditable browsing history.
CCTV and a security guard 24/7, recording every visitor's identity. Strictly controlled access.
Taking hardware away is forbidden and checked every evening. No work is permitted outside our offices.
Restricted WiFi network controlled by management, dedicated static IPv4 address, no WiFi access for smartphones. Social media and personal messaging forbidden.
UPS, long-life batteries and a backup generator: no power cuts, continuous production.
Beyond the technical side, a complete legal framework for your data, under Swiss responsibility.
We act as a processor (art. 28 GDPR and Swiss nFADP); you remain the controller, under a data processing agreement (DPA).
Data processed under the responsibility of Good-ID Sàrl, in Geneva. Switzerland benefits from an adequacy decision from the European Commission; the contract, the applicable law and the jurisdiction are Swiss.
Encryption, access management, client-segmented environments and logging, aligned with the principles of ISO/IEC 27001 (art. 32 GDPR).
Our data-protection framework is established and reviewed with our legal counsel, covering Swiss, French and European aspects.
Security also rests on people: signed commitments, limited access and strict rules.
NDAs and confidentiality clauses signed by every employee; employment contracts drafted by a law firm, with articles dedicated to data protection.
In the event of personal use of equipment or an attempt to extract data, criminal prosecution and compensation are contractually provided for.
Passwords for accounts and software are held solely by Good-ID management. No uncontrolled access.
Strict rules for using and maintaining equipment, and supervised access for service providers to workspaces.
Let's discuss your compliance requirements — reply within 24 to 48 h, from Geneva.